Containers Explained: How They Differ From Virtual Machines

A developer tests an application on a laptop, then sends a packaged version to a server. The package includes the application's runtime and libraries, reducing the familiar problem of software working on one machine but failing on another. That is one reason containers have become useful across software development and cloud infrastructure.
A container runs an application in an isolated environment using facilities provided by an operating system. An ordinary Linux container shares its host's kernel, the core that manages processes and hardware access. A virtual machine, or VM, runs a guest operating system with its own kernel on virtualized hardware.
That difference explains much of their behavior. Containers package and separate applications; VMs provide a boundary around a fuller operating system environment. Both still depend on the infrastructure and configuration around them.
What a container includes
A container image can package application code, a language runtime, libraries, supporting files, and a default command. These are the pieces that would otherwise need to be installed consistently wherever the application runs.
The image might include files from a Linux distribution, but it does not bring a separately running Linux kernel. An Ubuntu-based image can therefore run on a compatible Linux host using a different distribution. It uses the host kernel while providing its own collection of user-space files.
This is a useful distinction when people describe a container as a tiny computer. The application can see an environment that looks separate, yet its processes still rely on a shared kernel underneath.
Docker is one widely used tool for building and running these packages. It is not another name for the entire concept: other tools and runtimes also work with containers.
An image is a template; a container is an instance
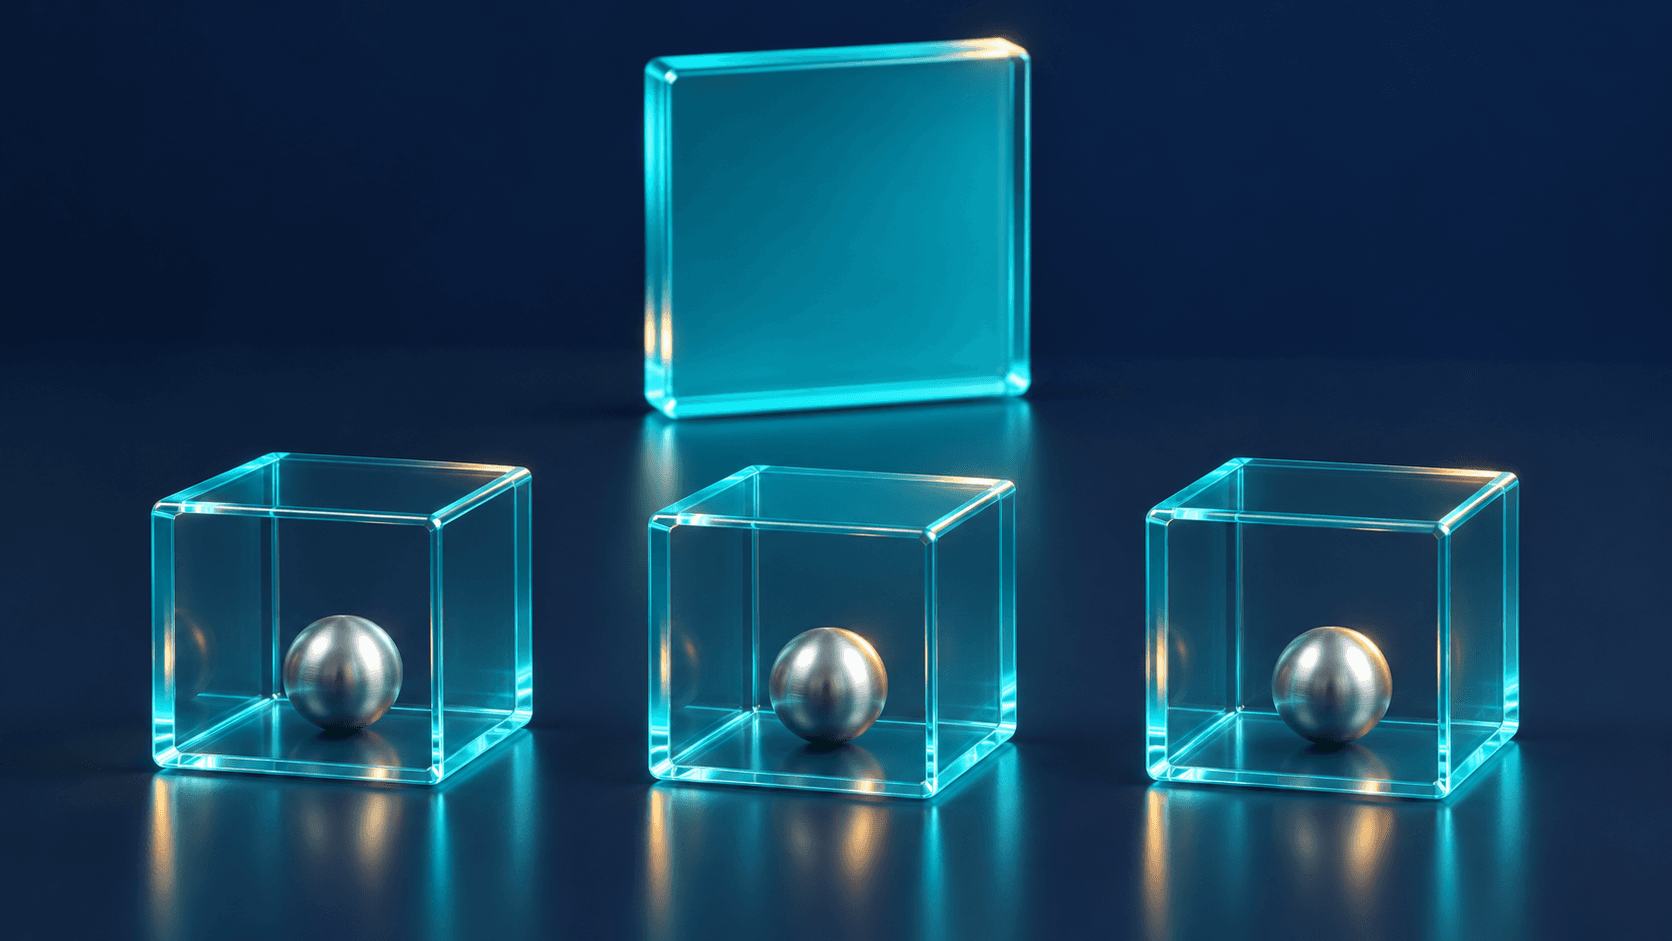
An image is a read-only template. A container is a runnable instance created from it, with runtime settings and a writable layer for changes. Starting several containers from one image does not make them one process or give them a single shared writable layer.
The illustration represents reuse through separate instances. In practice, each instance can receive different configuration, network connections, and storage mounts. Those choices influence behavior even when the image is identical.
Images are commonly stored in a registry, from which machines can pull them. A tag is a convenient name for an image reference, but it can be moved to different content. Even a tag that looks like a version number is not inherently immutable.
A digest identifies particular image content. Pinning a digest helps a team control what it deploys, but it also requires a deliberate update process. An old pinned image does not acquire security fixes merely because its original publisher releases a newer one.
How a virtual machine differs
A VM receives virtualized computing resources through a hypervisor. Its guest operating system runs its own kernel, along with the application and dependencies installed inside it.
Several ordinary containers on a Linux machine instead share one kernel. Avoiding a separate guest operating system for every application can reduce overhead and startup work. Actual resource use still depends on the workload, image, runtime, and host; the container label alone does not guarantee a faster application.
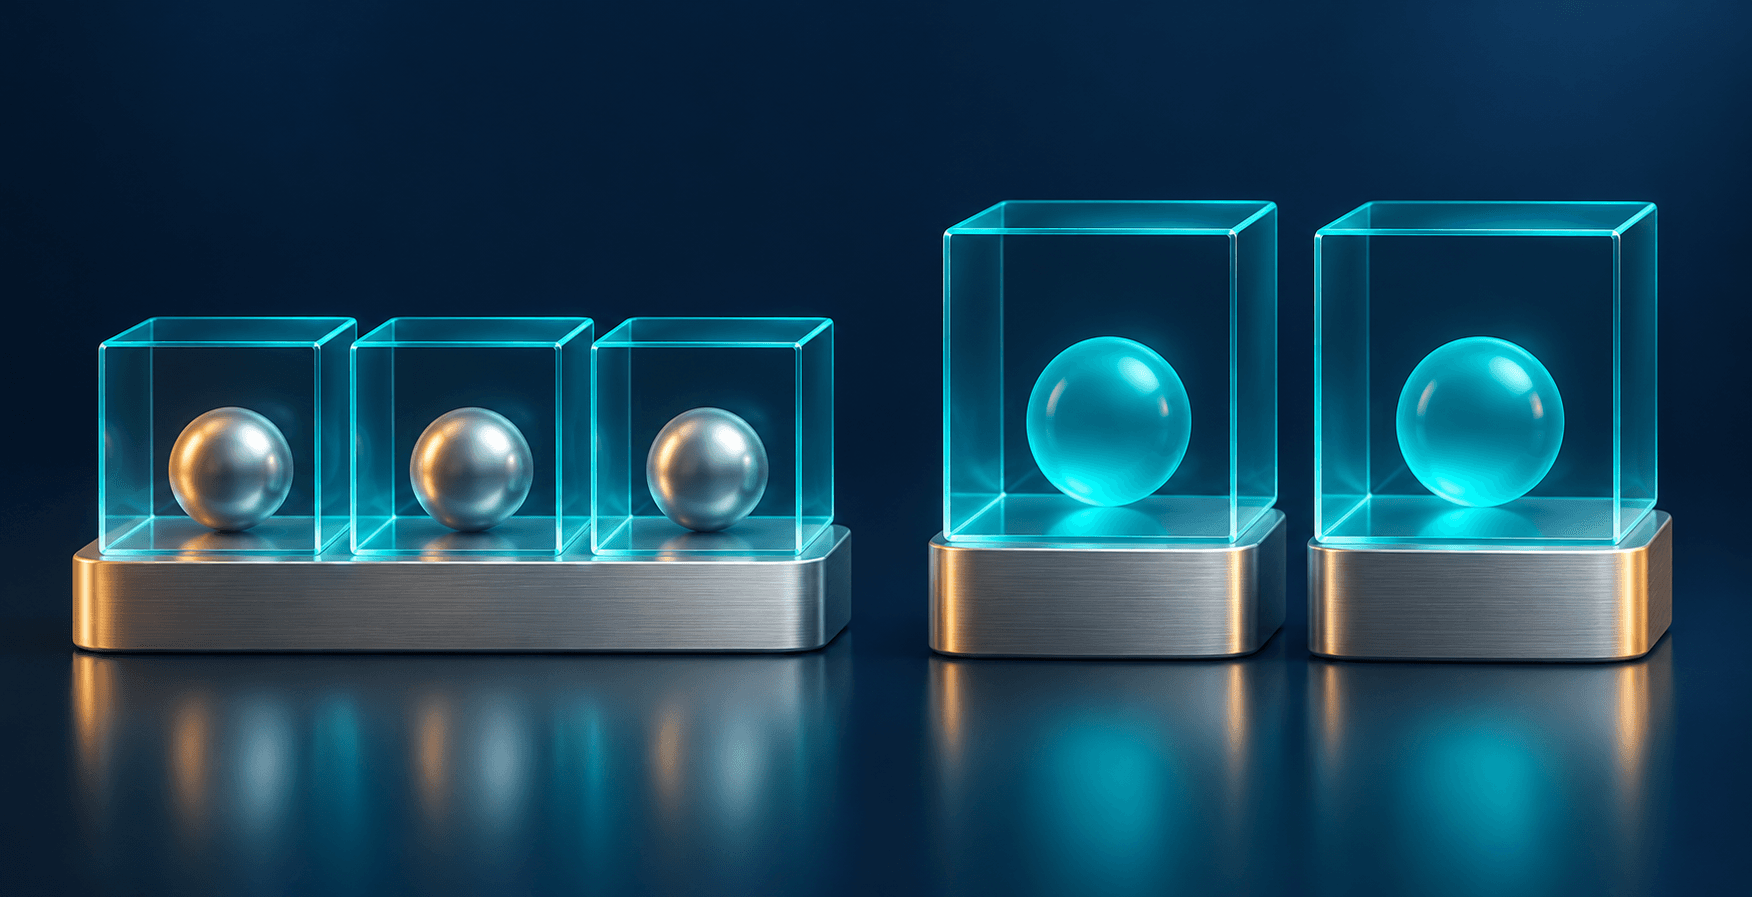
The header illustration uses a shared base beneath small chambers and separate bases beneath larger chambers as a metaphor. It does not depict literal hardware partitions or a measured performance comparison.
Containers and VMs also work together. A cloud VM can host multiple containers, combining a guest operating system boundary with convenient application packaging. Our cloud computing infrastructure guide provides the wider context for those layers.
Some container systems add VM-based isolation around workloads. The shared-kernel description applies to ordinary process containers, rather than every product that accepts a container image.
What isolation actually controls
On Linux, namespaces give processes separate views of resources such as process identifiers, network interfaces, and mounts. Control groups, often called cgroups, support resource accounting and limits.
These mechanisms help stop applications from casually colliding with one another. They do not eliminate the need to choose sensible permissions and resource settings. Docker containers, for example, have no CPU or memory limits by default; operators must configure appropriate constraints.
A container given broad host directory access can reach the files exposed through that mount. Privileged execution and access to the container engine's control socket can grant extensive authority. A neat package is not evidence that running it is harmless.
The shared kernel is also part of the security boundary. Its vulnerabilities and the runtime's configuration matter to every workload relying on it. VMs introduce a different boundary, but their hypervisors, guest systems, and management tools still require maintenance.
Our explanation of WebAssembly's execution boundary examines another approach to contained execution. The useful comparison is which resources a workload can reach and how access is enforced, rather than whether both technologies are called sandboxes.
Portability has requirements
Packaging dependencies removes one source of variation. It does not remove every difference between machines.
A Linux container still needs a compatible Linux execution environment. On macOS, tools such as Docker Desktop provide a Linux VM for Linux containers. That supporting layer is doing real work even when the interface makes launching a container feel simple.
Processor architecture matters too. An image built for one architecture does not become native code for another just because it is containerized. A multi-platform image can group platform-specific variants under one reference. Emulation offers another route, with its own compatibility and performance considerations.
Applications also need their expected settings and services. Missing credentials, an unreachable database, or a different storage mount can break the same image on a new host. Portability improves when a team documents and validates those requirements alongside the image.
Persistent data needs its own plan
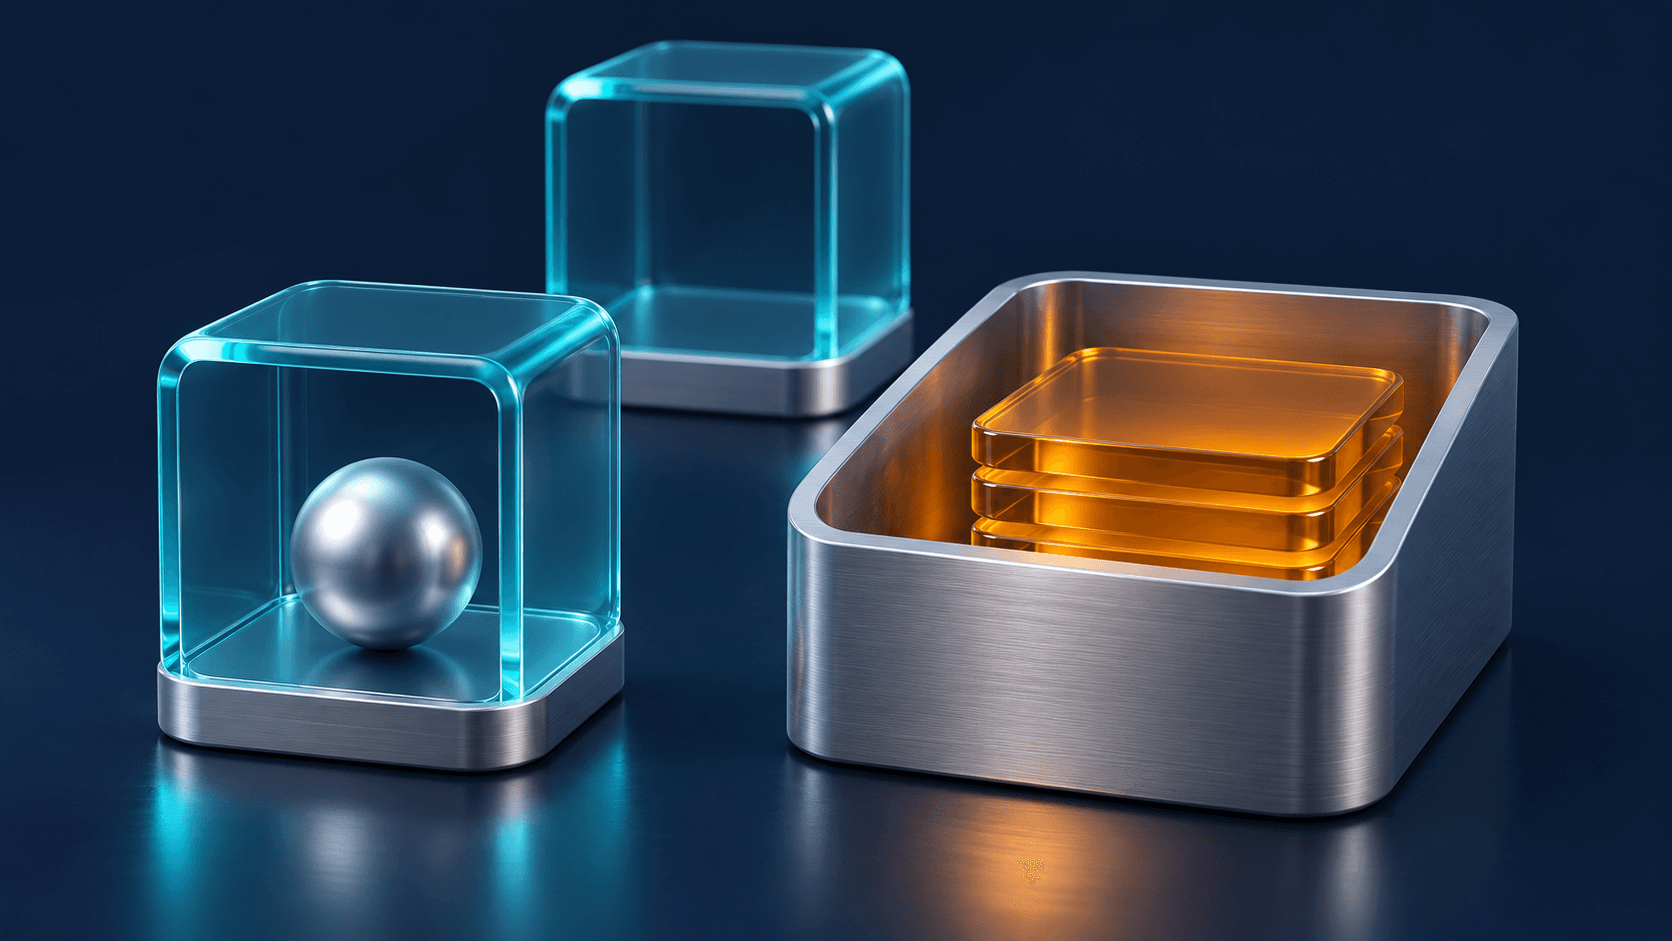
An application's writable container layer is tied to that container. Stopping and restarting the same container does not inherently erase the layer. Removing the container does.
Data that must outlive replacement therefore needs an independent location. A named volume can persist separately from a container. A bind mount can expose a host directory, while an external database or storage service provides another arrangement.
The storage illustration represents that separation. It does not imply that a volume is automatically backed up, replicated, or available on another machine. Persistence, backup, and recovery answer different questions.
Consider a hypothetical photo service. Its application instances can be replaced from an updated image, while uploaded photos remain in separately managed storage. The deployment still needs to reconnect that storage correctly and recover it if the underlying system fails.
Updating the package is operational work
A common update workflow is to rebuild an image with updated application code and dependencies, test it, and replace running instances. Retaining an old image can help a rollback, but database changes and stored data may require separate compatibility planning.
Operators should know where images come from, which versions are approved, and what privileges they receive. Vulnerability scanning can identify known problems; it does not certify every behavior in an image.
Likewise, a digest establishes content identity rather than publisher trust. Signing can add evidence about origin and integrity, subject to verification rules. Our guide to what digital signatures actually prove explains why correctly signed software can still contain dangerous behavior or bugs.
Choosing the appropriate boundary
Start with the workload and operating responsibilities:
- Package a service consistently. Containers can keep runtime dependencies together and make replacing application instances repeatable.
- Run a separate operating system environment. A VM can provide its own guest kernel when compatibility or isolation requirements call for that boundary.
- Combine both where useful. Hosting containers inside VMs is a normal design, rather than a contradiction.
- Match management tools to the scale. A few containers do not require Kubernetes. Compose can describe a multi-service application; Kubernetes adds orchestration capabilities for managing containerized workloads and services.
Before deployment, identify what can be replaced, what must persist, which resources are shared, and who maintains each layer. Containers become easier to reason about when their packaging convenience is paired with clear decisions about the system underneath.