Encrypted DNS Explained: What Private Lookups Actually Protect

Your browser offers a setting called secure DNS. Your phone may call something similar private DNS. Both sound as though they make browsing private, but the protection is more specific: they encrypt a connection used to look up internet names.
Encrypted DNS helps prevent observers on that connection from reading or changing the lookup traffic. It does not hide everything you do online, and the service answering your questions still needs to read them.
Understanding that boundary makes the setting more useful. You can choose a resolver deliberately, check which applications are covered, and avoid mistaking one protected step for an anonymous internet connection.
The lookup that happens before the connection
The Domain Name System, or DNS, connects names that people recognize with information that computers use. A common request asks for the network address associated with a website's hostname.
Your device usually sends that question to a recursive resolver. The resolver can return an answer it has cached or ask other DNS servers to find the information. Your browser can then connect to the destination.
DNS does more than find web servers, and a lookup is not a complete browsing record. Apps make background requests; pages load resources from several names; caches can avoid new requests. Nevertheless, a sequence of queries can reveal a great deal about the services a device uses.
Traditional DNS commonly sends queries and responses without transport encryption. Someone able to observe that network path may read the names even when the subsequent website connection uses HTTPS. Protecting the page transfer does not automatically protect the earlier lookup.
How encrypted DNS changes the exchange
In a typical encrypted setup, the basic sequence becomes:
- A client selects a compatible resolver. The client might be a browser, the operating system, or another application.
- It establishes a protected connection. A properly authenticated setup also checks that the server is the intended resolver.
- It sends the DNS question inside that connection. An observer along the protected path sees encrypted traffic rather than the readable question.
- The resolver reads the question and returns an answer. The response travels back through the protected connection.
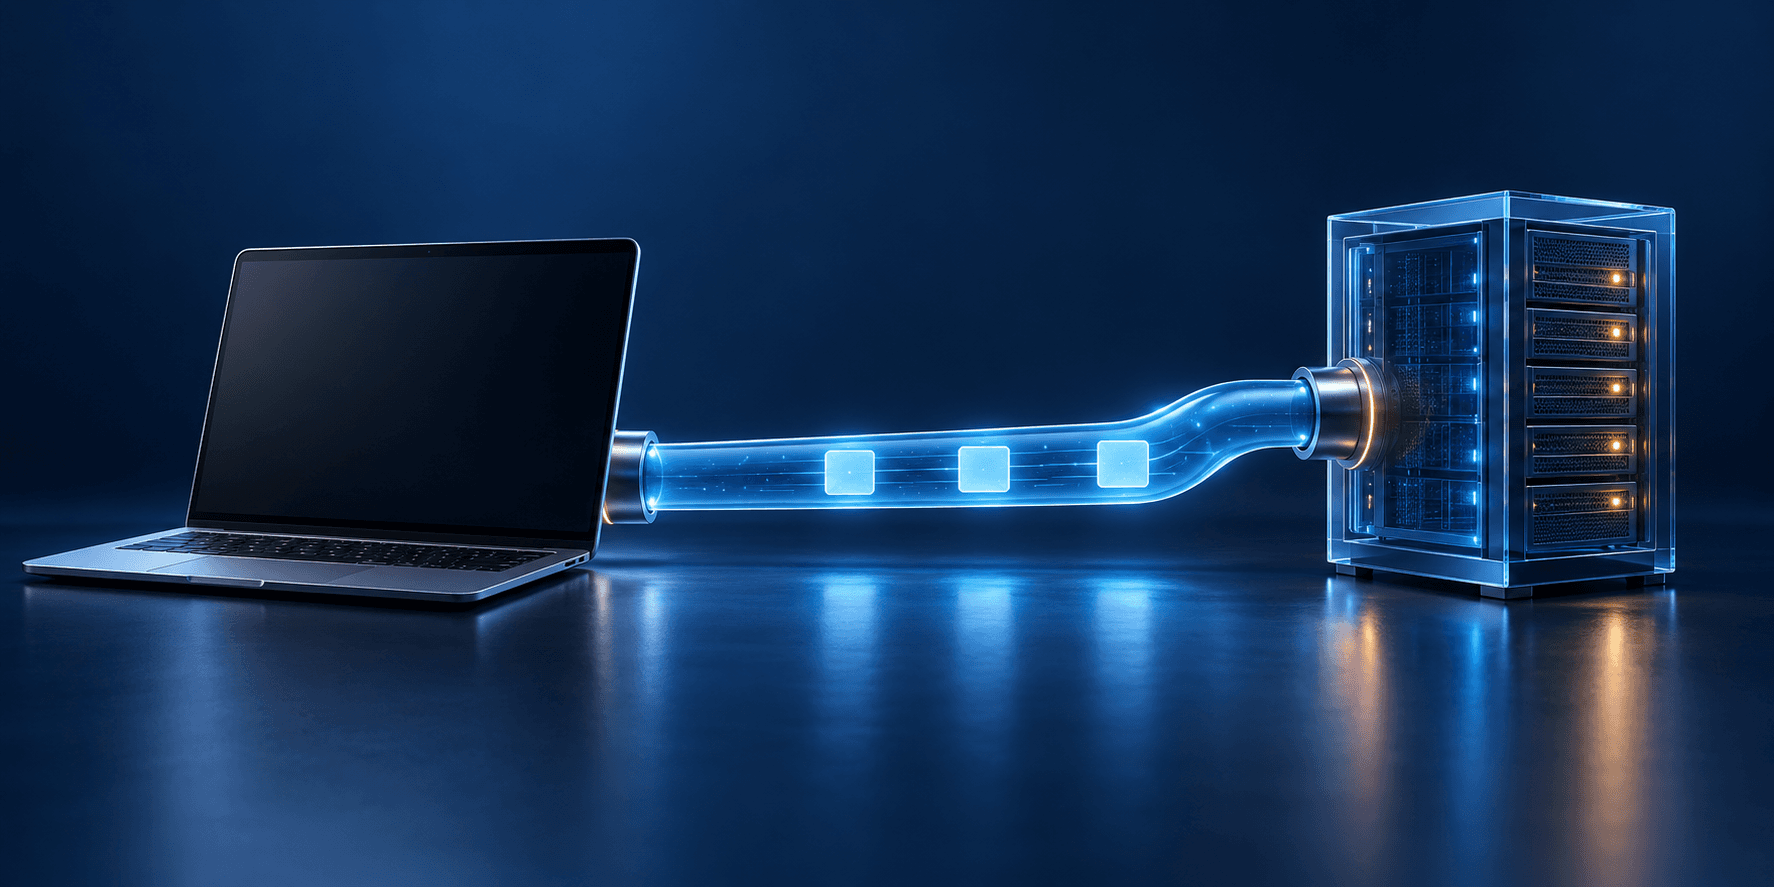
The header illustration represents this single protected journey. The conduit ends at the resolver because that is where this layer of encryption ends. Connections the resolver makes to other DNS servers have their own properties; enabling encryption on your device does not automatically encrypt every later step.
This is the same habit of identifying endpoints that matters when understanding end-to-end encryption. Here, the resolver is an intended reader of the lookup. It is not a delivery service kept blind to the question.
DNS over HTTPS and DNS over TLS
Two names appear frequently in settings and documentation.
DNS over HTTPS, or DoH, carries DNS requests and responses in HTTPS exchanges. It normally uses the same network port as ordinary secure web traffic. Browsers can implement it directly, although it is not limited to browsers.
DNS over TLS, or DoT, carries DNS traffic over a dedicated TLS connection, normally using port 853. TLS is the security technology also used by HTTPS. DoT gives DNS its own recognizable encrypted connection rather than wrapping the request in an HTTP exchange.
Both can protect lookup traffic in transit. The distinction does not make one a universal privacy winner: server authentication, provider practices, application coverage, and fallback behavior all matter.
Also separate the resolver address from the connection method. Entering a different DNS server's numeric address changes where questions go. By itself, that does not establish that they travel using DoH or DoT. Look for an explicit encryption setting and check its status.
The resolver still sees the question
Encryption protects a journey, not the intentions of the party at its destination. With ordinary DoH or DoT, the resolver can see the queried names and normally the source network address from which the connection arrives.
Changing resolvers can therefore move trust from a local network or internet provider to another operator. Using the existing resolver with encryption can improve transport protection without changing that operator. Neither arrangement removes the need to understand who runs the service.
Read its published privacy information with concrete questions in mind: what query information is retained, for how long, whether it is associated with identifying information, and whether it is shared or used for other purposes. A claim about encrypted transport answers none of those retention questions.
Ask about filtering too. A resolver may intentionally block certain categories or known malicious names. That can be a useful feature, but it is a separate policy choice from keeping the connection encrypted.
What private lookups do not hide
The connection to a website still has a destination network address. An internet provider or network observer may see that address, connection timing, and traffic volume. Shared infrastructure can make an address ambiguous, but encrypted DNS alone does not guarantee that the destination remains unknown.
The website still receives your connection. It can recognize a signed-in account, read cookies it is entitled to receive, and use other available signals. Our browser fingerprinting explainer describes recognition that does not depend on reading DNS traffic.
Encrypted DNS also leaves your public network address unchanged. A VPN changes the traffic path and introduces a different trust relationship; switching on DoH is not equivalent to switching on a VPN.
Nor does encryption establish that a destination is safe. An authenticated resolver can return information about a phishing site just as successfully as a legitimate one.
DNSSEC addresses another question: it uses signatures to support authentication and integrity checks for DNS data. It does not encrypt the query. DNSSEC and encrypted transport can work together, but neither should be mistaken for a judgment about the honesty of a website.
Check the scope and the fallback
A browser's secure DNS setting may apply only to that browser. Another app can use the operating system's resolver or its own DNS implementation. A device setting and a router setting can also protect different connections. Identify where the encrypted connection starts and ends rather than assuming that every setting covers the whole household.
Fallback deserves equal attention. Some modes prefer encryption but return to another resolver when it fails. Stricter modes can stop resolution and show an error instead. Those choices trade uninterrupted access against a stronger requirement that the protected path remain available.
Firefox provides a concrete example: its documented Default Protection can fall back to default resolvers, while Max Protection warns when the secure resolver cannot be reached. The documentation also describes how network conditions and managed policies affect operation. Setting names and behavior vary between products, so inspect the current explanation beside the control.
On a work or school device, consult the administrator before changing the resolver. Internal names, approved filtering, and VPN routing may depend on the existing configuration. A public resolver might not know an internal service's name. That is a configuration boundary to understand, not evidence that encryption is broken.
A practical verification checklist
Before relying on a new setting:
- Name the goal. Decide whether you want to protect lookups from local observation, change resolver operators, or both.
- Identify the operator. Check its privacy and filtering policies instead of choosing solely by a reassuring label.
- Confirm encryption is active. Use the application's status indicator or documented diagnostic method, rather than treating a saved address as proof.
- Check other applications. Establish whether they share the protected resolver path or have separate settings.
- Read the failure behavior. Know whether an unavailable resolver causes a warning, an encrypted alternative, or a return to unencrypted DNS.
- Try your normal environments. Check home connectivity, mobile data, and any approved VPN or managed network you use. Record the previous setting so troubleshooting is straightforward.
These checks reflect the broader zero trust principle of verifying access and assumptions. A successful page load proves that something resolved the name; it does not prove which resolver or transport was used.
Encrypted DNS closes a real exposure in the lookup path. Its value becomes clearer when you can say which connection is encrypted, who receives the readable question, and what happens when that connection fails.